通常我都會配合 ffuf 和指定辭典使用:
SecLists/Fuzzing/LFI/LFI-Jhaddix.txt:我會最優先使用的PayloadsAllTheThings/Directory\ Traversal/Intruder/dotdotpwn.txt:測的東西比 Jhaddix 多很多,但很容易誤報。
Nineveh
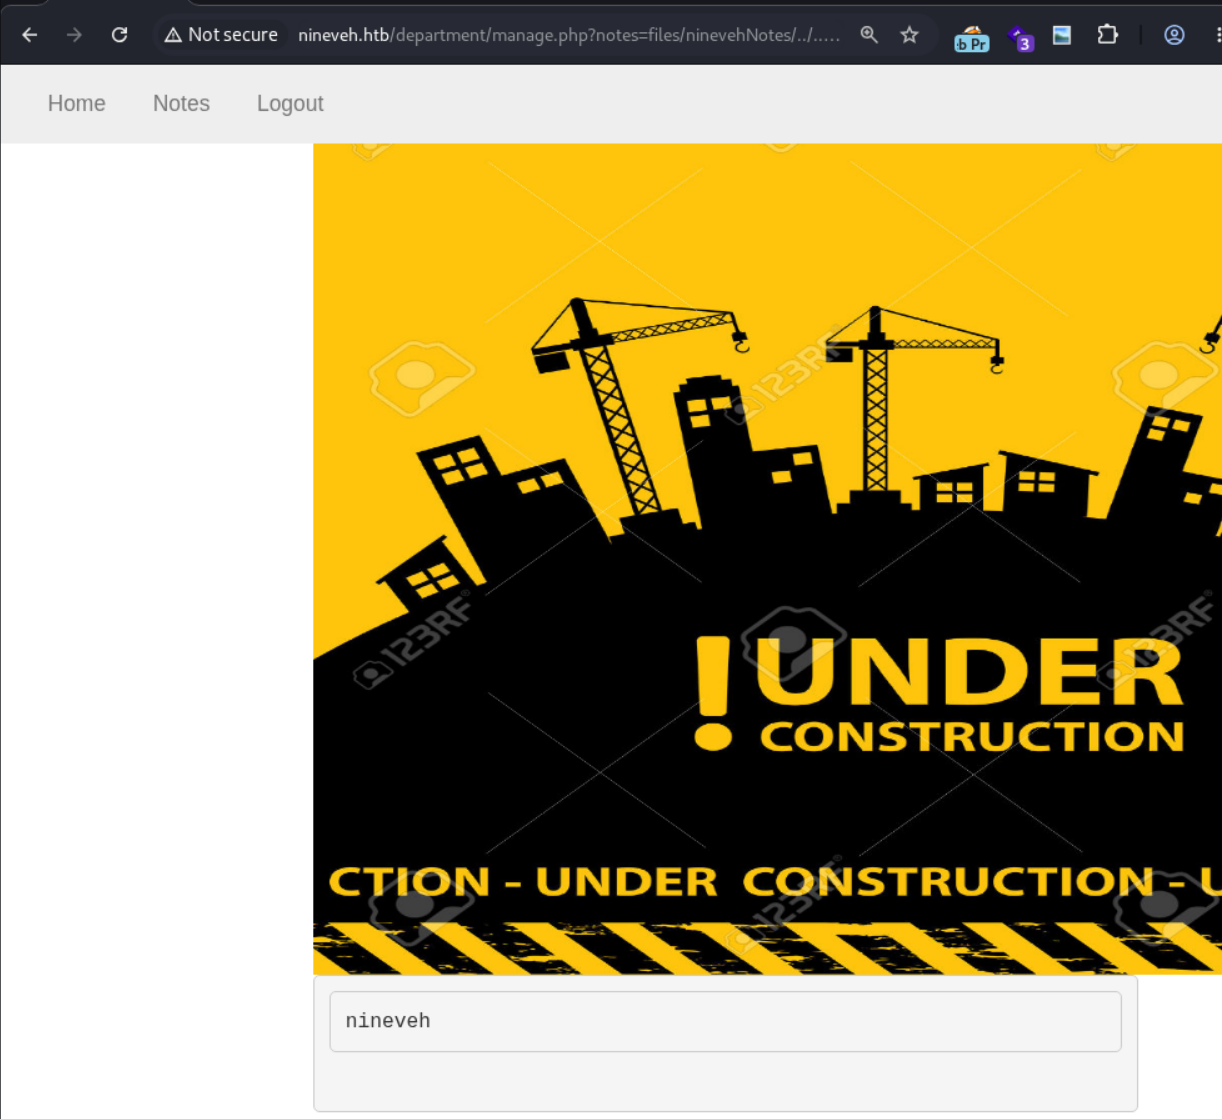
在 Nineveh 靶機中,我們發現 http://nineveh.htb/department/manage.php?notes=files/ninevehNotes.txt 存在 File Inclusion 漏洞,只要以 http://nineveh.htb/department/manage.php?notes=files/ninevehNotes/../../../../../../ 為底即可存取本機上 www-data 有權讀取的任何檔案,例如 /etc/hostname:
它的 PHP 是這麼寫的:
<?php
        $file = @$_GET['notes'];
        if (strlen($file) > 55)
            exit('File name too long.');
        $fileName = basename($file);
        if (!strpos($file, 'ninevehNotes'))
            exit('No Note is selected.');
        echo '<pre>';
        include ($file);
        echo '</pre>';
?>
緩解措施
- 改以白名單映射。使用者輸入僅作為識別碼,由伺服器端對應到實際路徑,不讓輸入內容參與路徑組合。
- 若必須接受路徑,先以
realpath()正規化,再驗證結果仍位於基準目錄之內,才進行讀取。 - 於 PHP 設定中關閉
allow_url_include與allow_url_fopen,避免本機檔案包含被提升為遠端檔案包含。 - 以最小權限執行網頁服務,縮小即使遭利用也能讀取的檔案範圍。